cwashingtonblue team · soc

Hi, I'm

ChristoferWashington

SOC analyst who builds the lab, writes the detections and automates the response.

CySA+, PenTest+ and Security+ certified, with a B.S. in Cybersecurity. I run a three-node Proxmox lab with my own SIEM, detection rules mapped to MITRE ATT&CK and self-healing automation.

Open to SOC analyst & GRC roles · Daytona Beach or remote

~/securxlab
$ whoami
Christofer Washington
$ cat roles.txt
Cybersecurity Professional
$ ls certs/
A+  Network+  Security+  CySA+  PenTest+  ITIL v4 Foundation  Linux Essentials
$ ▍

Live · updated hourly

Global threat activity

Real attack sources seen by SANS Internet Storm Center honeypots worldwide, plus scans and sign-in attacks blocked by this site in real time.

–attack sources
–countries
–blocked here · 24h

Loading threat data…

Data: SANS Internet Storm Center (DShield) · GeoIP by DB-IP

Featured work

All projects

Homelab

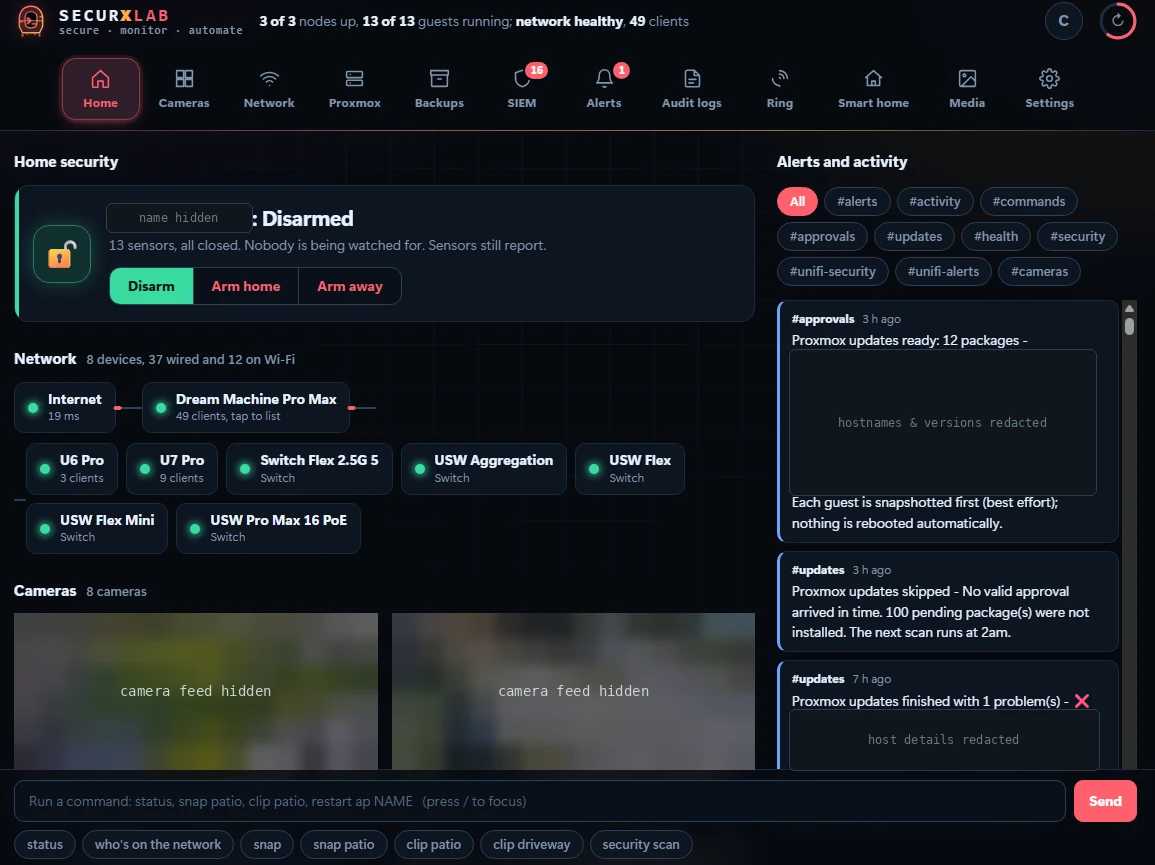
Securxlab — Homelab SOC & Self-Healing Command Center

A self-built security operations dashboard for my homelab: SIEM with MITRE ATT&CK-mapped detections, alert triage and threat intel, plus Proxmox, UniFi and camera control, all driven by n8n automation with human-in-the-loop approvals.

Custom detection rules, each with a severity
13
MITRE ATT&CK techniques mapped across 5 tactics
7
Security events ingested & correlated per day
~1.4k
Read the case study
Homelab

3-Node Proxmox Cluster

The foundation of my lab: a three-node Proxmox VE cluster running my SIEM, automation, web and home services as VMs and containers, with approval-gated patching, a self-healing watchdog and key-only SSH.

Proxmox VEKVMLXCDocker+5

Read write-up
Cyber Lab

Elastic SIEM + MISP

A dedicated Elastic SIEM for my lab: Filebeat ships host logs from every Proxmox node over TLS, automation events land in their own index, and MISP adds threat intelligence, all so I can investigate the way a SOC analyst does.

Elasticsearch 8KibanaFilebeatMISP+3

Read write-up
Cyber Lab

n8n + Discord Ops Bot

AI-assisted n8n workflows that watch my Proxmox cluster around the clock: they restart failed guests, scan for updates and wait for my approval, diagnose errors with an LLM, and report through the dashboard, with Discord as the fallback.

n8nProxmox APIOllama (llama3)Claude API+5

Read write-up
Cyber Lab

This Website: a Hardened, Self-Hosted Portfolio CMS

I replaced WordPress with a lightweight CMS I host myself: a private editor behind password + TOTP 2FA, an AES-256 encrypted database, a strict content security policy, a locked-down container and a one-command installer, with seven layers of defense in depth.

Node.jsExpressSQLCipherArgon2id+6

Read write-up

What I work on

The tools I use daily in my lab, and what I do with them.

Network Security & Monitoring

I use packet analysis and signature-based detection tools to identify anomalous traffic patterns and validate the effectiveness of firewall rules in my lab environment.

WiresharkNmaptcpdumpSnortZeek

Infrastructure & Virtualization

I architect and maintain a high-availability Proxmox cluster to host isolated security environments, ensuring consistent uptime for monitoring services and malware analysis.

Proxmox VEVMware ESXiDockerTrueNAS

Automation & Scripting

I develop custom scripts to automate repetitive security tasks, including parsing system logs for failed login attempts and generating daily threat reports.

PythonPowerShellBash

Defensive Operations (Blue Teaming)

I manage edge security and centralized logging to provide full-stack visibility into my network, enabling proactive threat detection and rapid incident response.

pfSense/OPNsenseSplunkWazuh

Offensive Security & OSINT

I perform controlled vulnerability assessments and OSINT investigations to identify potential attack vectors and strengthen the overall security posture of my infrastructure.

Kali LinuxBurp SuitetheHarvester

From the lab notebook

All posts

Hiring for your SOC or GRC role?

I am currently looking for my next opportunity as a SOC Analyst or GRC Analyst where I can streamline operations and secure critical infrastructure. Let's talk!